

1·
1 month agoIs it tab to pay you want or store tickets and membership cards in it.
Is it tab to pay you want or store tickets and membership cards in it.
On the paid version there should be no problem with codec.

The Securities and Exchange Commission (SEC) bought access to what it described as more than a billion airline ticketing records, related to not just U.S. domestic flights or those landing in the country, but also flights between foreign countries, according to SEC documents obtained by 404 Media. A group of the world’s airlines, including Delta, United, and American, previously sold the data under the company name ARC; that is where the SEC bought the data from.
ARC, or the Airlines Reporting Corporation, stopped selling airline ticketing records after repeated coverage from 404 Media and pressure from lawmakers last year. But the newly obtained records provide additional insight into the breadth of data that airlines were selling without their customers’ knowledge, and that law enforcement agencies were tapping into, likely without a warrant.
“ARC’s ticketing data includes not only US domestic flights and international flights to/from the US, but also flights entirely between or within foreign countries,” one of the documents obtained by 404 Media reads. 404 Media obtained them through a Freedom of Information Act (FOIA) request with the SEC.
The data includes each passengers’ name, their credit card number used to buy the ticket, the departure and arrival cities of their travel, the date of their flight, the flight number, and the “selling agency,” likely referring to the travel agency the person used, according to the documents. ARC obtained its data by acting as the conduit between airlines and travel agencies. Whenever someone booked a flight with a travel agency like Expedia or Kayak, ARC received information about that booking and then resold it as part of its data broker business.
ARC’s Travel Intelligence Program (TIP), as the data product was called, was also capable of sending daily search results related to a specific list of names, the document says. “ARC sends daily reports regarding any air ticketing purchased by individuals over the prior 24 hours),” it adds. The document says SEC required access to 1-25 daily searches through this alert service.
The SEC did not respond to a request for comment.
ARC previously told 404 Media that TIP “was established by ARC after the September 11, 2001, terrorist attacks and has since been used by the U.S. intelligence and law enforcement community to support national security and prevent criminal activity with bipartisan support. Over the years, TIP has likely contributed to the prevention and apprehension of criminals involved in human trafficking, drug trafficking, money laundering, sex trafficking, national security threats, terrorism and other imminent threats of harm to the United States.”
deleted by creator
I just don’t see the point. Android is open source and there already exist alternatives to the things google play services dose. Instead of the googles push nonfiction system(FCM) there is unifiedpush https://unifiedpush.org/ and alternative apps stores like f-droid or accrescent https://accrescent.app/.
I hope you a right about the security improving but i am not so optimistic of it even coming close to Android.
Linux phones are way less secure than Android phones. There already exist phone os like grapheneos or lineageos or calyxos that degoogle. Linux desktop and phone don’t sandbox apps so if you install one malicious app it has access to all files on the phone your camera and so on. Even if you use flatpak the flatpak sandbox is weaker(easier to break out of) and the app dev of the flatpak app decide what permission it should have unlike on android where the user does so with major permissions like camera.
I have watched the futo video and i think don’t think its very likely it will become a paid feature. The CTO said they would want to have the registration require some kind of cost but it was almost certainly meant as a computing cost not money. Link to the same video in case you can’t play it https://i.imgur.com/QMDjn7T.mp4
Thanks.
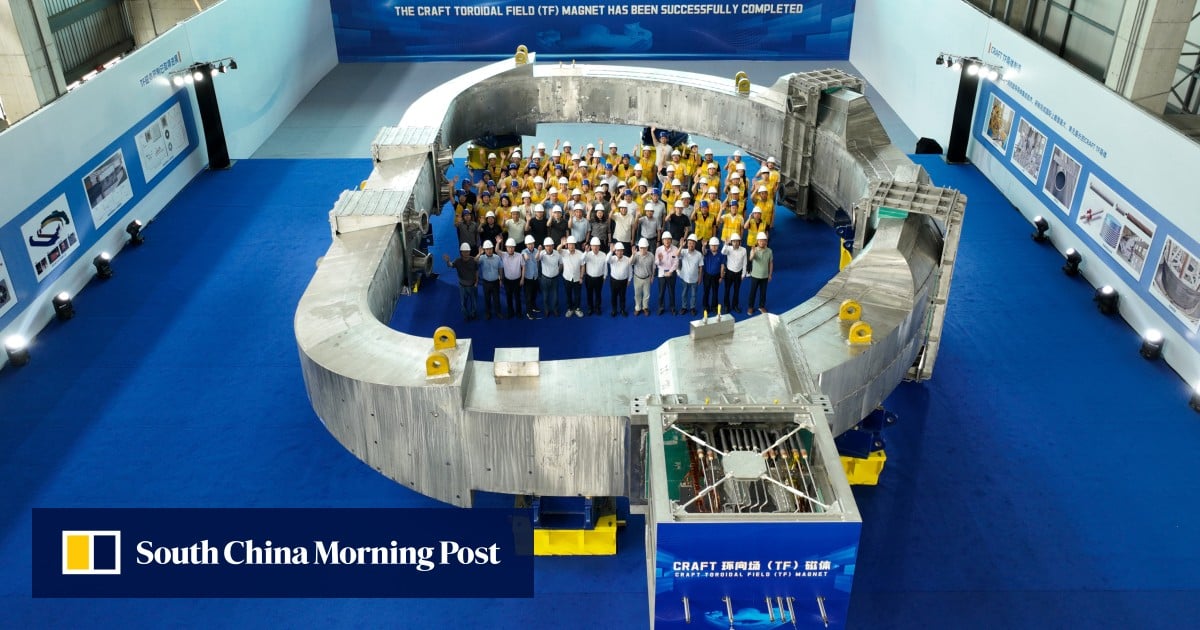
There is also this https://economictimes.indiatimes.com/news/new-updates/china-completes-worlds-largest-582-tonne-superconducting-magnet-for-artificial-sun/articleshow/132711254.cms with some more details but i don’t know if its the most trustworthy source
https://zerevia.com/product/t-shirt/1838893-bombing-kids-is-not-self-defense here but might just be someone trying to capitalizes on the news story.
Ecosia is not that great for privacy “Your IP address and search terms are automatically shared with our search partners, Microsoft Bing or Google, when you search.” https://www.ecosia.org/privacy
deleted by creator
Same. With 404 media its luckily only an email no name or date of birth. But it still suck you have to.
Here is the full article click on the arrow to display it
In charging a man for allegedly typing in a duress password which wiped his privacy-focused GrapheneOS phone, the U.S. government is trying to intimidate other activists from protecting their data and participating in social movements, Samuel Tunick, the man charged, told 404 Media in an interview on Tuesday.
The case of Tunick, who participated in the Stop Cop City movement in Atlanta, has resonated across privacy and civil liberties circles. 404 Media first broke news of the case in December. Last week, The Guardian reported additional details including from a court hearing in the case. The maximum sentence for the alleged crime is five years in federal prison.
“I hope people understand that the charges against me are meant to intimidate people against protecting their data and their privacy, and the government hopes to set a precedent that no one has the right to privacy,” Tunick told 404 Media in a conference call with his federal public defender Matthew Dodge.
Asked about his reaction to the wide attention his case has gotten, Tunick said it’s “a little surprising, but encouraging that people seem to care about this issue.”
In January 2025, Tunick was returning to the U.S. from a vacation in the Dominican Republic. Dodge explained that Department of Homeland Security (DHS) officers called the airport ahead, said Tunick was coming through, and asked officers to stop him. “‘We want you to get his phone and search his phone,’” the officers said in Dodge’s retelling.
The officers asked Tunick if they could search his bags, and he said no. The agents searched them anyway and found nothing unlawful, Dodge said. Tunick declined to be patted down, but again the agents searched him anyway, and they found nothing improper, Dodge said. Then the agents said they wanted to search his phone. Tunick declined and asked for his lawyer multiple times. Finally, the agents asked for his phone, and gave a pretence of searching for child abuse imagery, according to Dodge.
Tunick gave a code which an officer typed into the device, Dodge said. Rather than unlocking the phone, the device “went to a blank screen” and displayed the GrapheneOS logo, Dodge explained. GrapheneOS, a mobile operating system that has a wealth of privacy and security upgrades, has a duress password feature that “will irreversibly wipe the device,” according to GrapheneOS’s website. Asked for comment, Daniel Micay, the founder of GrapheneOS, pointed 404 Media to a recently published overview on the operating system’s defenses against data extraction.
With the phone inaccessible, Tunick was free to go and left the airport. Around a year later he was indicted for allegedly destroying “the digital contents of a Google Pixel” phone. Dodge said he only found one other case using the same law, a drug trafficking investigation. “This is extraordinarily rare,” Dodge said.
“The agents tried to rig this game by making this all come to a head at the airport,” he added. Ordinarily authorities would need a warrant to search the contents of someone’s phone; at an airport, those protections often do not apply. “They could have asked the judge for a search warrant for Sam’s phone if they thought they had evidence of a crime. They didn’t do that,” Dodge added.
A Customs and Border Protection (CBP) spokesperson told 404 Media in an email “All travelers are subject to inspection to ensure compliance with U.S. laws. These inspections, including questioning and the rare search of electronic devices, are conducted on a case-by-case basis, taking into account factors such as travel history and law enforcement alerts.”
The U.S. Attorney’s Office declined to comment.
In the interview with 404 Media, Tunick put his prosecution squarely in the context of the sprawling cases against other Stop Cop City protesters and other activists in the U.S. more broadly. He pointed to the RICO charges against dozens of people, with 61 of those charges later being dropped (some still faced domestic terrorism charges). Tunick said that case had him listed as an unindicted co-conspirator.
Tunick also pointed to the landmark domestic terrorism Prairieland case in which people protested an ICE facility (one of those people received a 100 year sentence for shooting a police officer), and the newly signed National Security Presidential Memorandum (NSPM-7) which the ACLU says seeks to target nonprofits and activists.
“Many of us had a suspicion that this was kind of the testing ground for a new, more heavy-handed trend in policing in America. And that does seem to be in fact the case: that Atlanta was sort of the testing ground for a more authoritarian, heavy-handed approach to social movements,” Tunick said. As 404 Media reported in March, Proton Mail provided user data that helped the FBI unmask an anonymous Stop Cop City protester.
Tunick described to 404 Media how before the airport encounter, he tried to get a job at a Christmas tree lot. The job involved going onto the property of a school, so it required a background check. Despite not having a criminal record, he failed the background check, Tunick said. He went to the Atlanta Public Schools office to find out why, and was eventually given a phone number and told to contact the FBI, Tunick recalled. He also said a hidden camera was placed outside a house he used to live in.
Later, he found out from his lawyer that a tracker had been placed on his car. He also learned his cellphone records were subpoenaed, and he said he got an email from Google saying his Gmail account had also been subpoenaed.
“They really just tried to dig up anything they could on me and they didn’t find anything,” Tunick said. “At this point, it almost seems like it’s just intended to make my life miserable and discourage participation in any sort of advocacy or activism.”
Initially, Tunick was shocked by the phone wiping charge, he said. Once that feeling faded, he said the charges made sense in the arc of government “repression that we’ve seen over the last year and a half.”
Regarding his case about being charged for allegedly wiping a phone, Tunick said, “I just hope that other citizens and activists understand that this is not a precedent that we should allow to be set.”
Update: this piece has been updated to include a statement from CBP and that the U.S. Attorney’s Office declined to comment.

Link to the screenshot. https://thelemmy.club/pictrs/image/30b71352-4e4d-4d9a-bdd9-0913abc89bc2.png

deleted by creator
They aren’t but it is the same as if you have been accused of murdering some one and you burn the car you are accused of moving the body to the river in.
Edit: I am not saying i think its how i should work but its the logic behind it
Alternative lemmy interface.


Alternative lemmy interface.
Yes. On that node it’s important to know that in many countries you can refuse to give up your password but if you erase the data it’s seen as destruction of evidence.




Cloudfare have many service a dns resolver is one of them. Quad9 only provide a dns resolver. When you visit a website and see Cloudfare thats has nothing to do with their dns resolver that is a complitly different service they provide to protect against ddos attacks.